05 / Malware Removal
WordPress site hacked? We'll clean it up.
WordPress malware removal for hacked sites, wherever they are hosted. We'll take a look for free and tell you what we find, then quote for the cleanup. Once you are happy to go ahead, we remove what got in and close the way in behind it.
- Free investigation
- Quote before any work
- Wherever it is hosted
- We find how they got in
- Written summary after
Signs your WordPress site has been hacked
Some hacks are obvious. Many are built not to be, and only show themselves to search engines or to visitors on certain devices, so the site can look perfectly normal to you.
Redirects you did not set up
Visitors, often only those on phones or arriving from Google, get sent to a spam, gambling or scam site.
A warning in Google or the browser
Google shows "This site may be hacked" in results, or the browser puts up a red warning page before anyone gets to your site.
Pages you never wrote
Search Google for your domain and you find pages in foreign languages or selling things you have never sold.
Read a real caseAdmin users you do not recognise
New administrator accounts in WordPress, or your own login suddenly no longer working.
Read a real caseA message from your host
Your hosting company has flagged malware, suspended the account, or reported it sending spam.
Read a real caseIt has gone down with a critical error
The site shows "There has been a critical error on this website" or a blank page, and nothing you changed explains it. Sometimes the hacker's own tools are what broke it.
Read a real caseCheckout or forms have stopped working
Payments will not load or enquiry forms fail. A hack can block them as a side effect of hiding its own pages.
Read a real caseSomething just feels off
The site has slowed right down, pop-ups appear that you did not add, or files have changed that nobody touched.
Tell us what you are seeing We take a look for free and tell you what we find.
A free look first. A quote before any work.
You know what is wrong and what it will cost before anything is cleaned or charged.
01
Tell us what you are seeing
Call or send us a message with the site address and what you have noticed. Screenshots of any warnings help.
02
We take a look, for free
We look at the files, the database and the user accounts to work out what has been changed and how far it has spread. Then we tell you what we found and quote for the cleanup, before any cleanup work starts.
03
We clean it up
Once you are happy to go ahead, we remove the malicious code and put the site back into a clean, working state.
A clean scan is not a clean site.
Security scanners are a useful first look, but they miss things. Malware injected into a WordPress core file can look like a perfectly ordinary file to a scanner while it quietly serves spam to Google.
So we do not stop at a scan. We look for everything that changed and every way back in, inside WordPress and outside it. Leaving one piece behind is how a site ends up hacked again a week later.
A scanner checks
- Known malware signatures
- Files that match something it has seen before
We check
- Every file compared with known-good copies
- Every file changed while the attacker had access
- The database and every user account
- Server keys, scheduled tasks and control panel tokens
- Other sites sharing the same hosting account
What a cleanup covers
Getting the malware out is half the job. The other half is making sure the attacker cannot simply walk back in.
Get a free look- 1Find and remove the malicious code, including anything hidden in WordPress core, plugin and theme files
- 2Remove rogue administrator accounts
- 3Restore affected files from a clean backup where one exists
- 4Close the entry point where we can identify it, such as an outdated or unlicensed plugin
- 5Check for ways back in outside WordPress, such as server keys, control panel tokens and other sites on the same hosting account
- 6Request removal of any search engine or browser blacklisting
- 7Send you a short written summary of what happened
Recent cleanups
Recent jobs, written up with the client's details taken out.
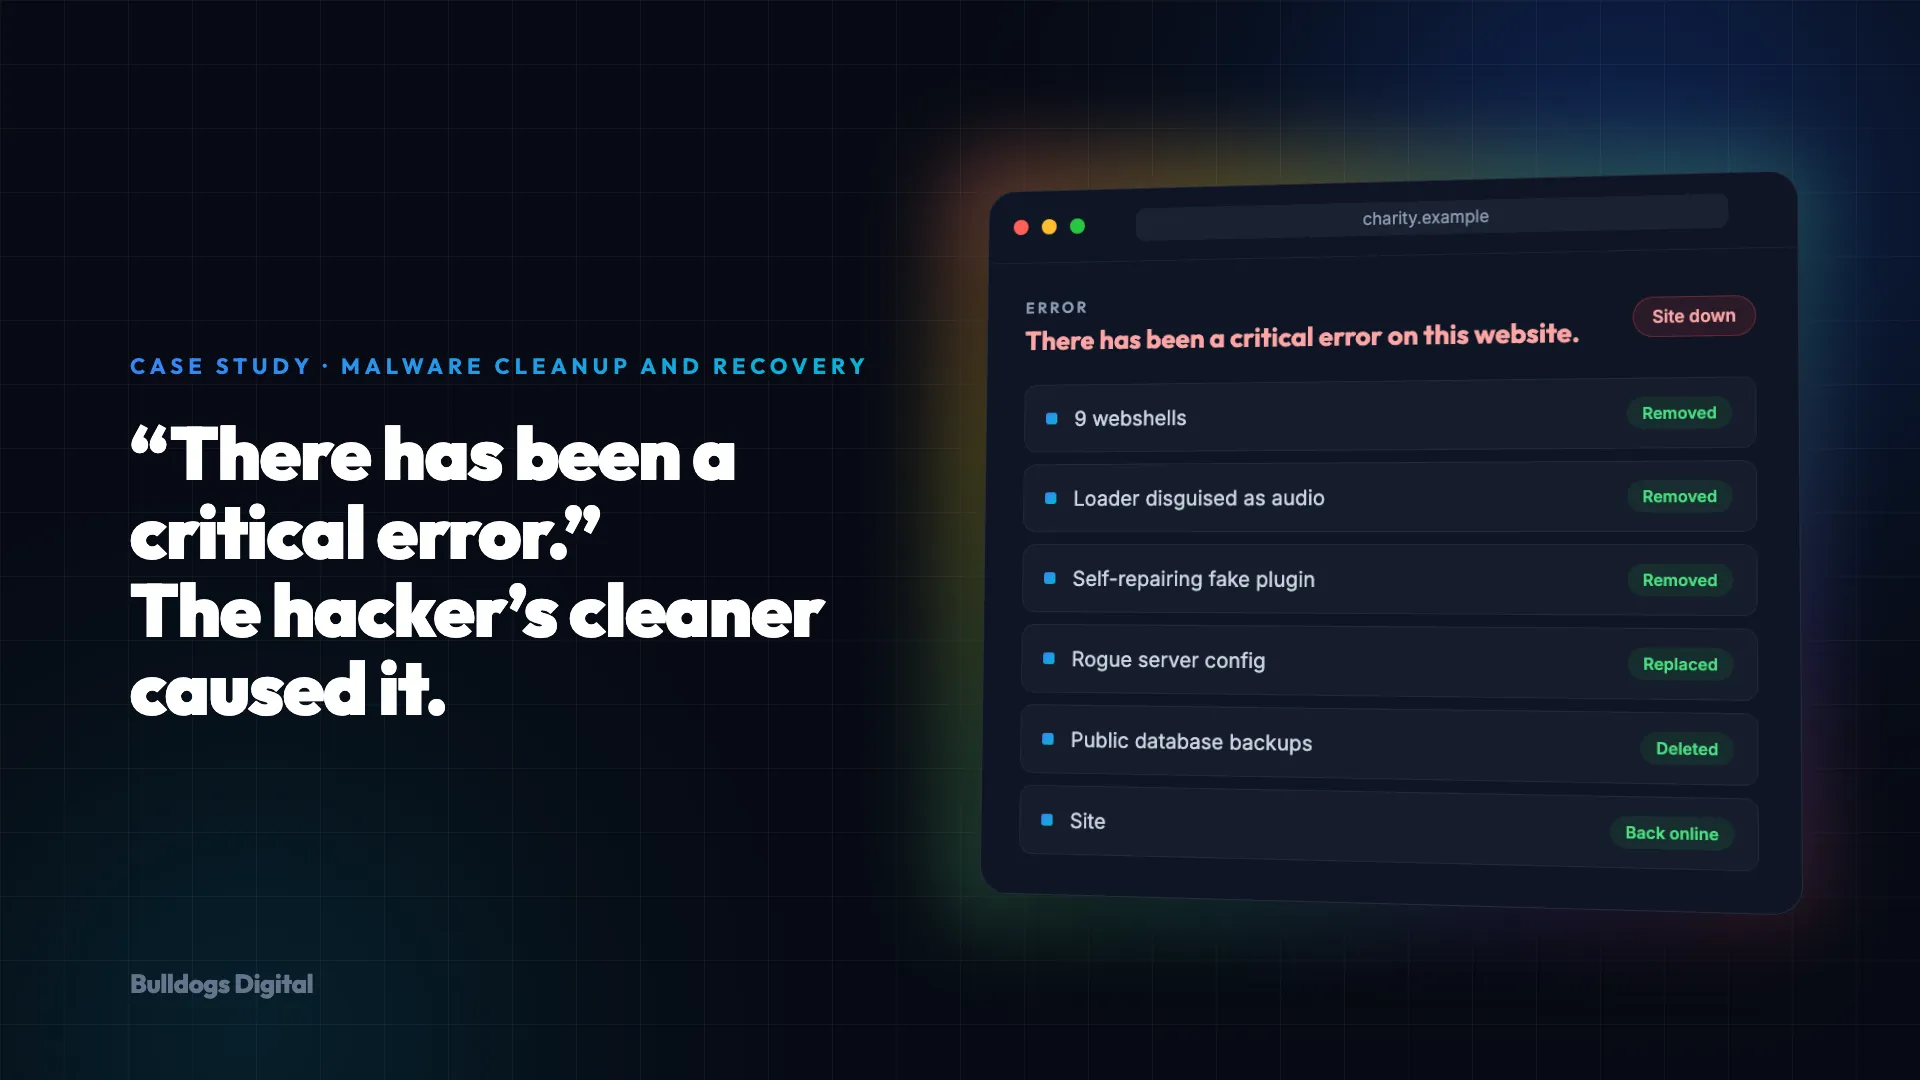
The malware "cleaner" that took a charity's website offline
Nine webshells, a backdoor that rewrote itself on every page load, and a site back online the same day we started.
Read the case study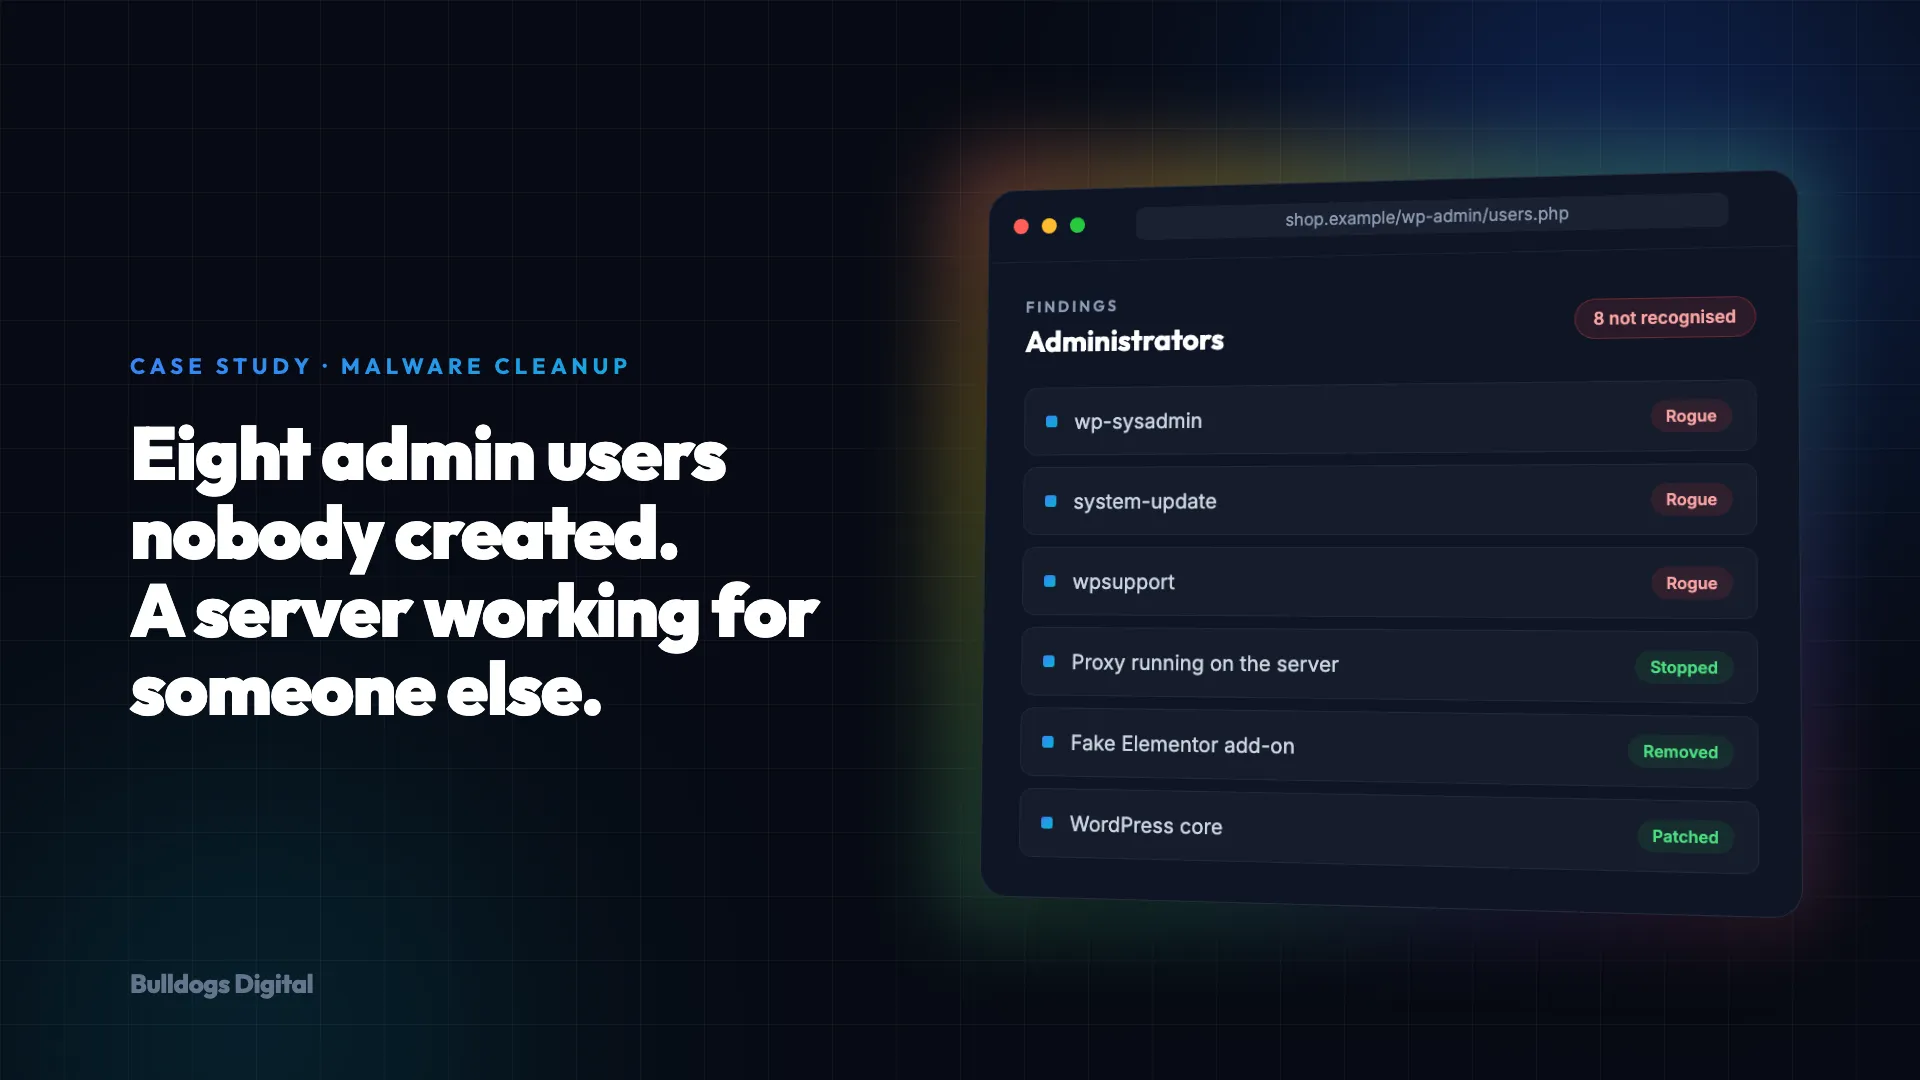
Eight admin users nobody created, and a server working for someone else
A flaw in WordPress core, and a program running outside the website that a restore would have missed.
Read the case study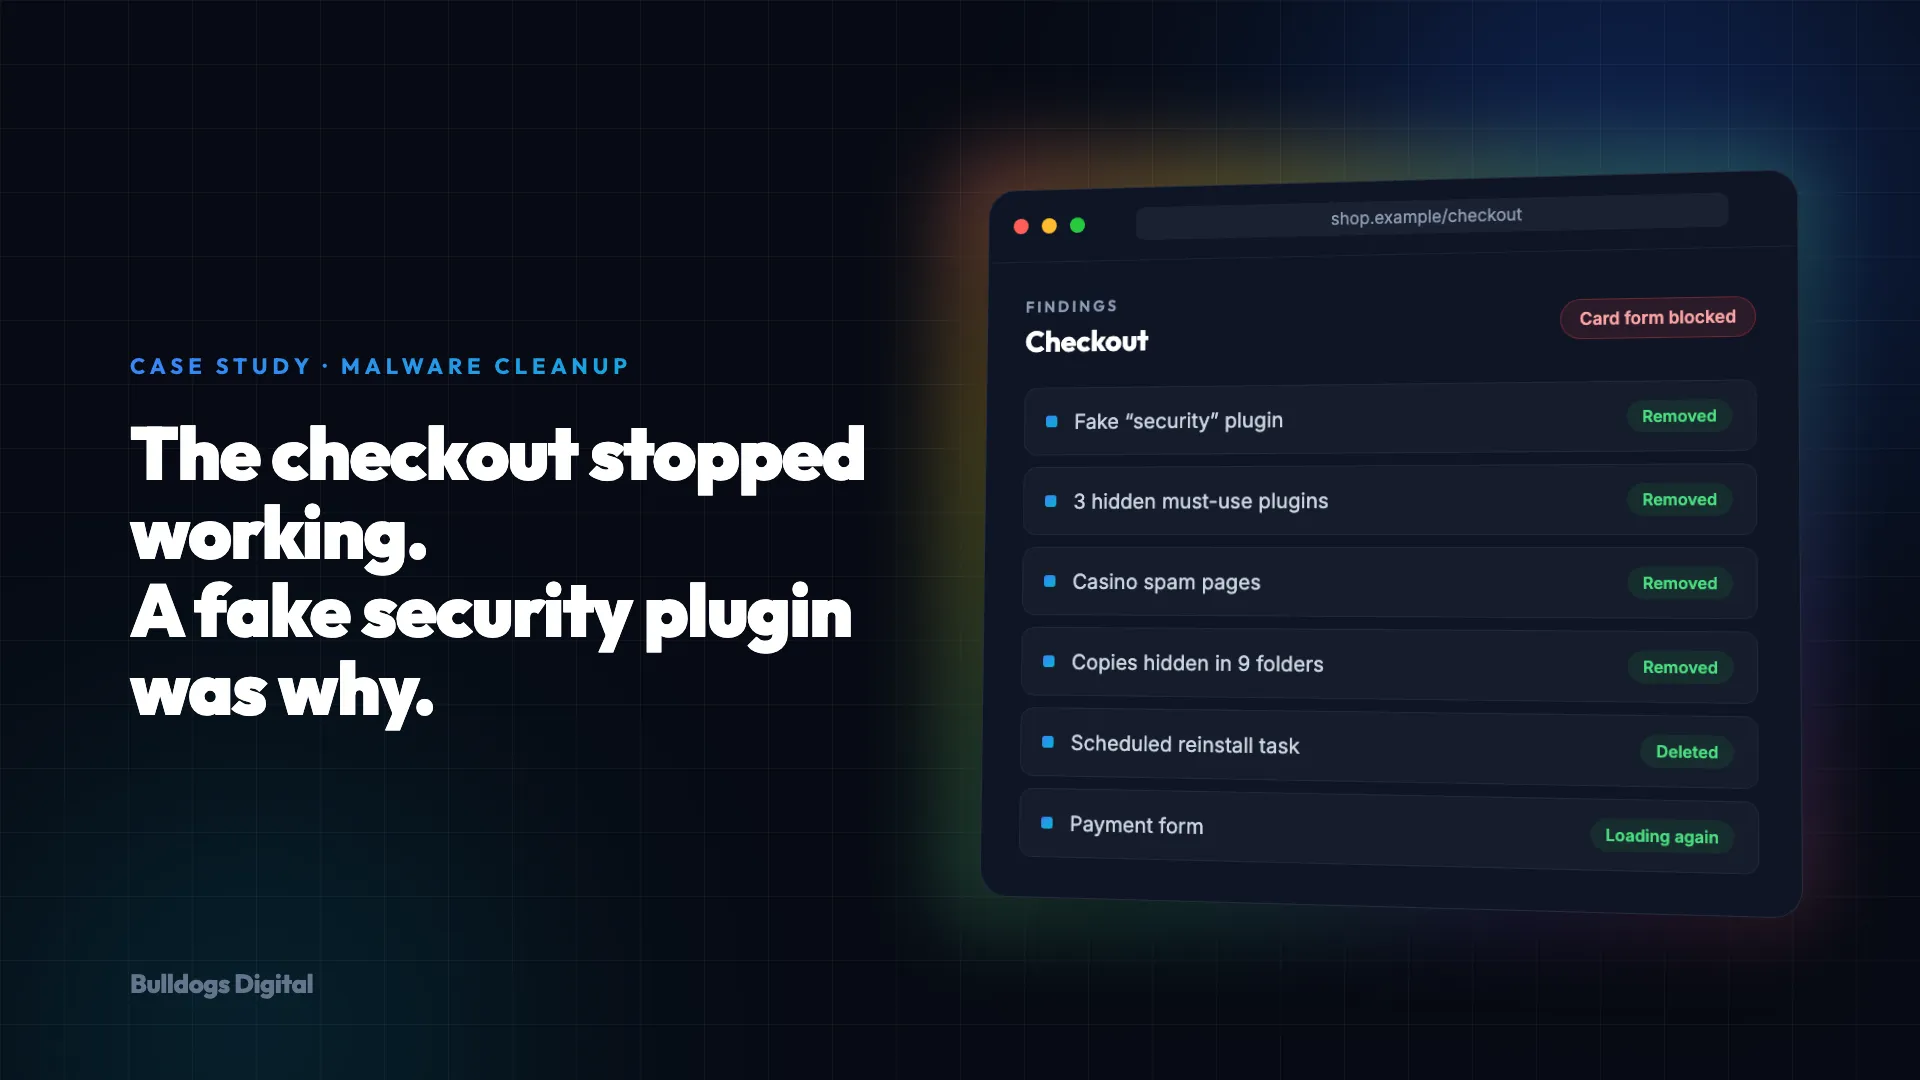
The fake security plugin that broke a shop's checkout
Casino spam, hidden copies in nine folders, and why the order you remove things in matters.
Read the case studyThen stay covered
Once your site is clean, move it to us on a WordPress maintenance plan and we move it across for free. We host it, keep it updated and monitor it, and if it is ever compromised again, the cleanup is included rather than another bill.
Cover only applies to sites we host, because we cannot protect a server we do not run. Already on a plan? You are covered, subject to our maintenance terms.
Common questions
How much does malware removal cost?
Taking a look costs nothing. We investigate for free, tell you what we find, then quote for the cleanup. The price depends on what we find, because a single infected plugin is a very different job from a site where the malware has spread through core files and the database. Nothing gets cleaned, and nothing is charged, until you have agreed the quote.
How quickly can you start?
Get in touch as soon as you notice something, because a hacked site tends to get worse rather than better. We cannot give a fixed timescale before we have looked, as it depends on what we find, but we will tell you honestly when we can start.
Do I have to move my hosting to you?
Not for the cleanup. We can clean up a WordPress site wherever it is hosted. Moving it to us only matters if you want to be covered afterwards, because we only cover sites we host. If you join one of our maintenance plans, we move the site across for free.
My hosting company says the site is clean now. Is it?
Maybe. Automated scanners are useful, but they miss things, and a clean scan is not proof of a clean site. Hacked sites are often reinfected because something was left behind, such as a modified core file, a hidden admin account or the original way in. That is why we check files against known-good copies rather than relying on a scan alone.
What if it keeps getting hacked?
Then something was left behind, almost always the original way in or a second one nobody found. It may not be in the website at all: we have found attackers coming back through server keys, control panel tokens and forgotten old sites on the same hosting account. Where a cleanup has already failed once, rebuilding the site from known-good copies is often the safer route, and we will tell you if we think that is where you are.
Can you stop it happening again?
We close the way in where we can identify it, which is the main thing that stops a reinfection. Nobody can honestly promise a site will never be hacked again. What we can offer is to host and maintain it afterwards, with updates, monitoring and future cleanups included in the plan.
What if the site cannot be recovered?
Occasionally there is no clean backup from before the hack and the damage runs too deep to clean. If that is where we end up, we will tell you plainly and quote separately for a rebuild. You will not be charged for a rebuild you did not agree to.
I am already on one of your maintenance plans. Am I covered?
Yes. If your site is hosted with us and your plan is active, cleanup is included at no extra charge, subject to the conditions in our maintenance terms. Just get in touch and we will get started.
Think your site has been hacked?
Send us your site address and what you are seeing. We will take a look and tell you what we find.
- 1We take a look, for free
- 2We tell you what we found and quote for the cleanup
- 3Nothing is cleaned or charged until you agree
Rather talk it through?
01903 252258